Introduction
As cyber threats continue to evolve, organizations need more than traditional security solutions to defend against sophisticated attackers. Modern cybercriminals use advanced techniques to gain unauthorized access, move laterally across networks, steal sensitive information, and disrupt business operations. Understanding how these attackers operate is essential for building effective cybersecurity defenses.
Definition
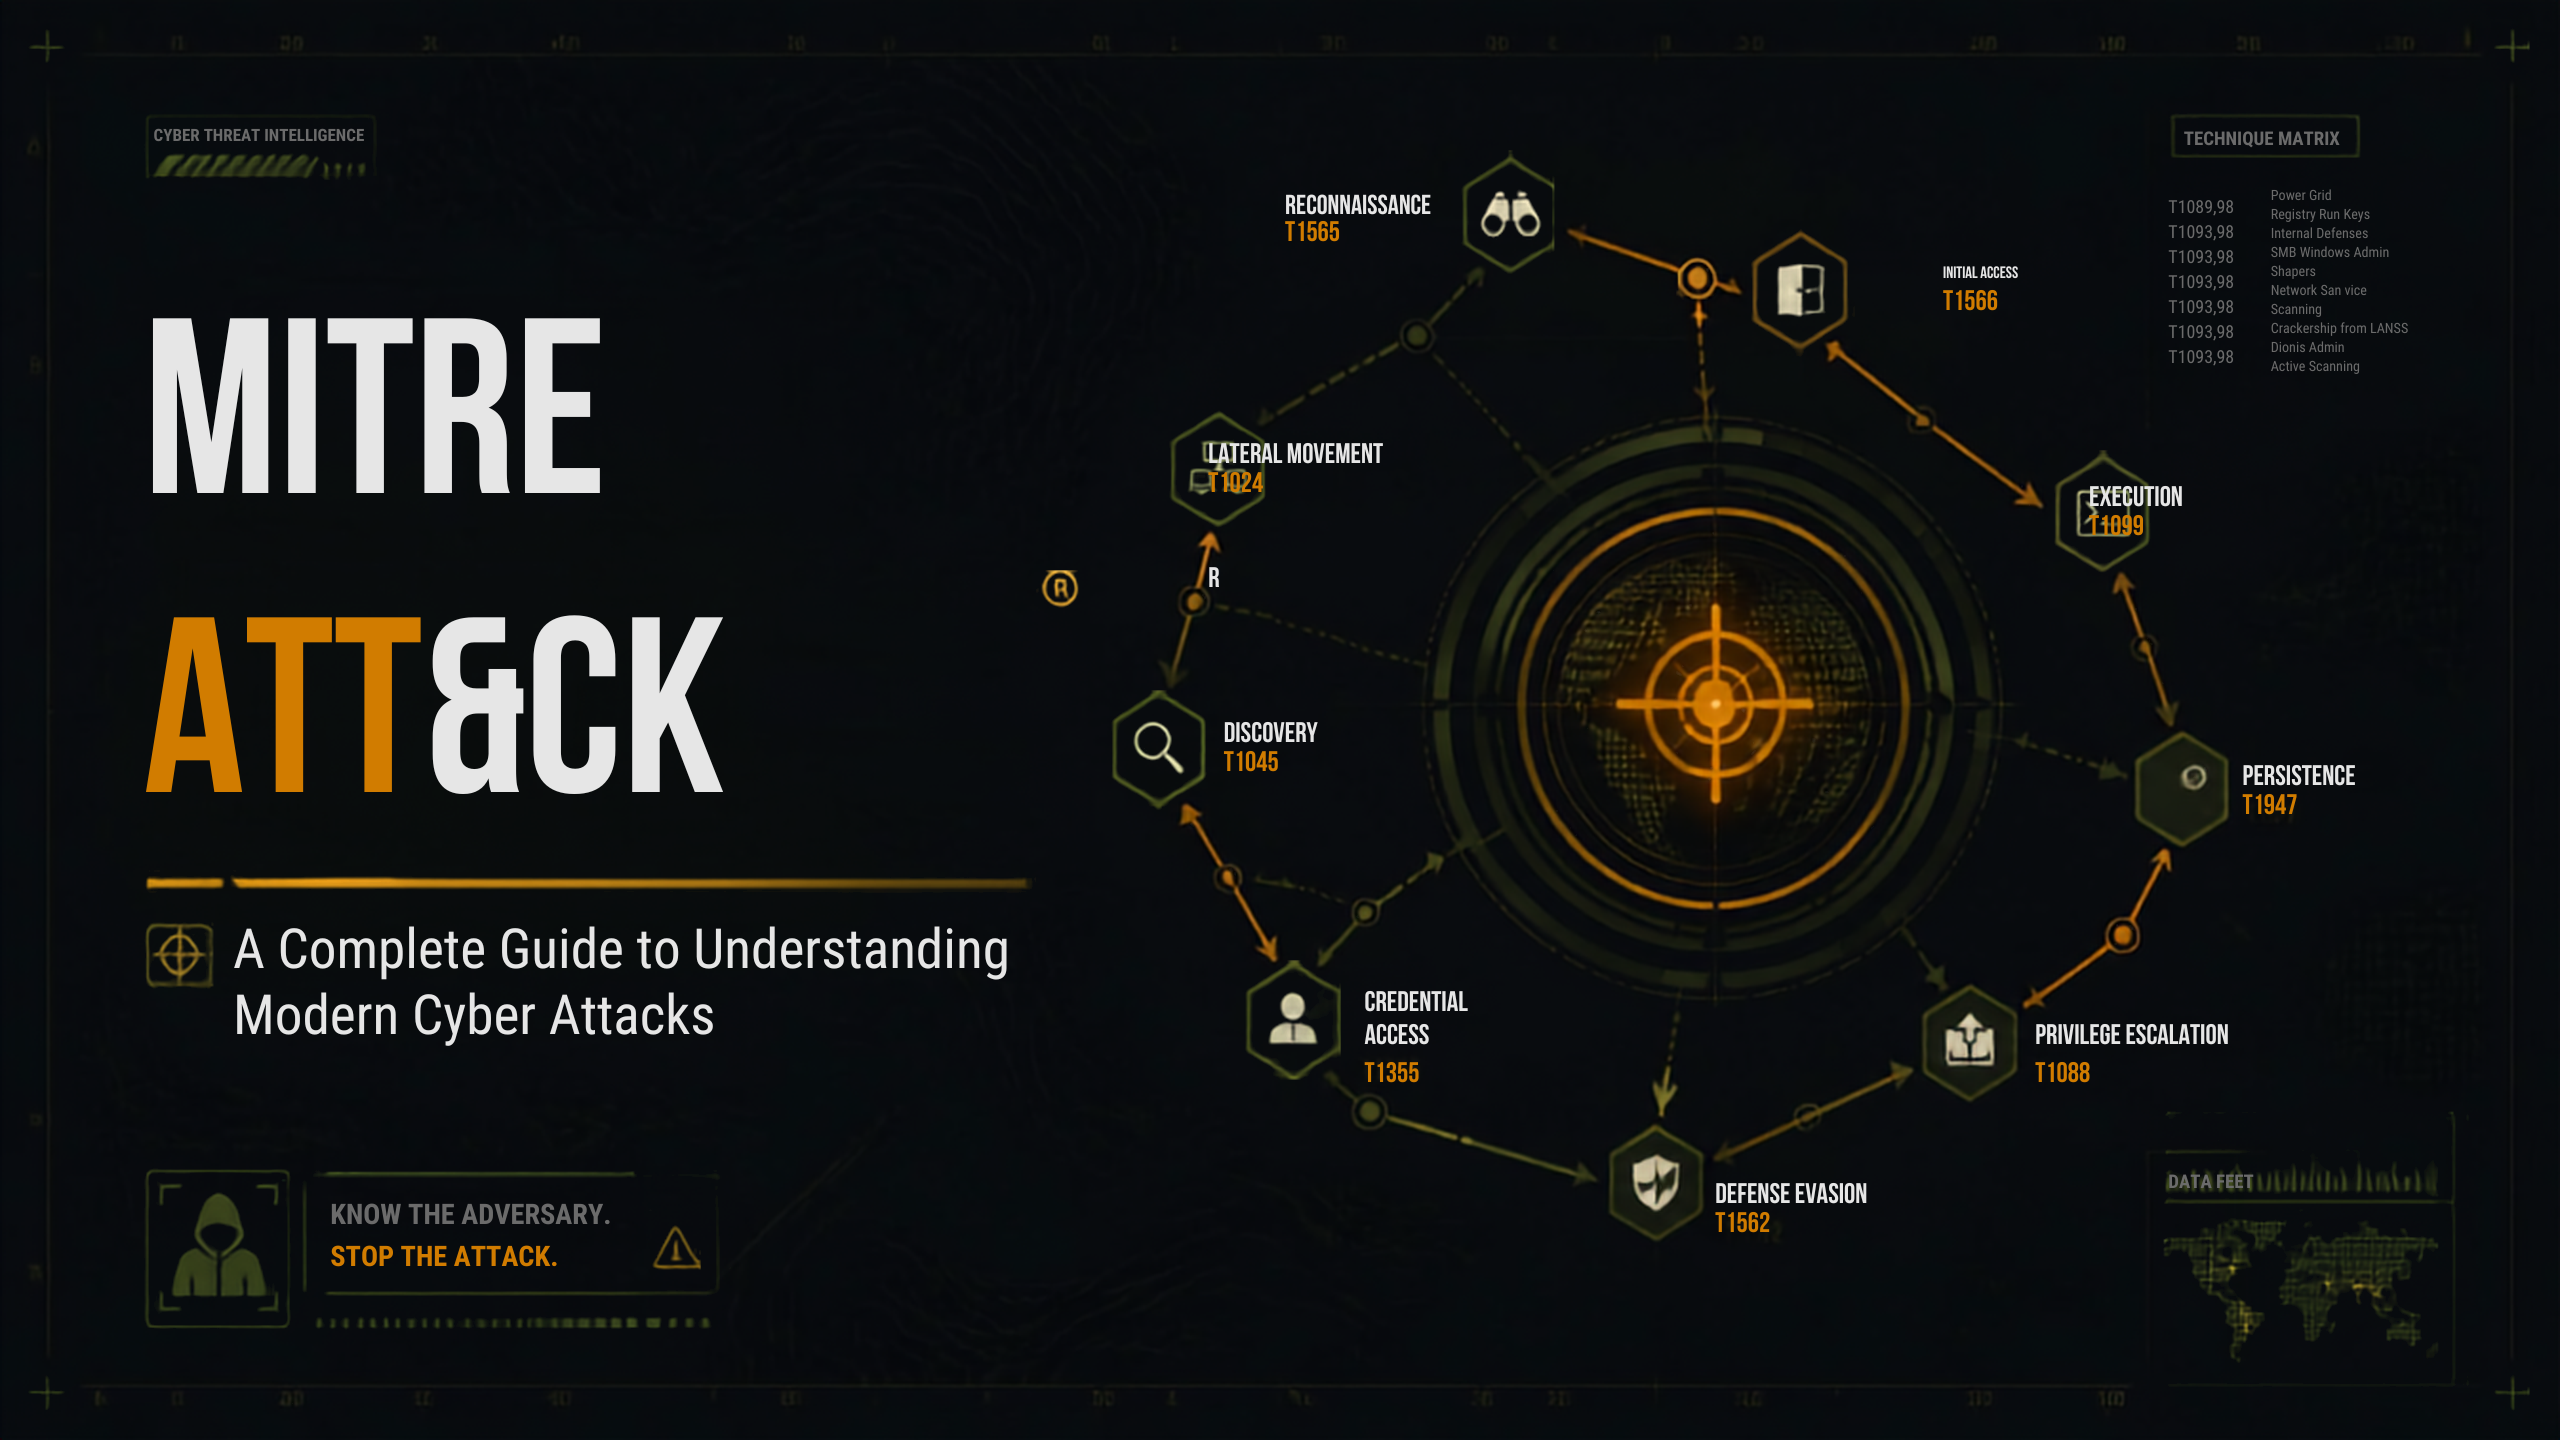
MITRE ATT&CK (Adversarial Tactics, Techniques, and Common Knowledge) is a globally recognized cybersecurity framework that provides a comprehensive knowledge base of attacker behaviors based on real-world observations.
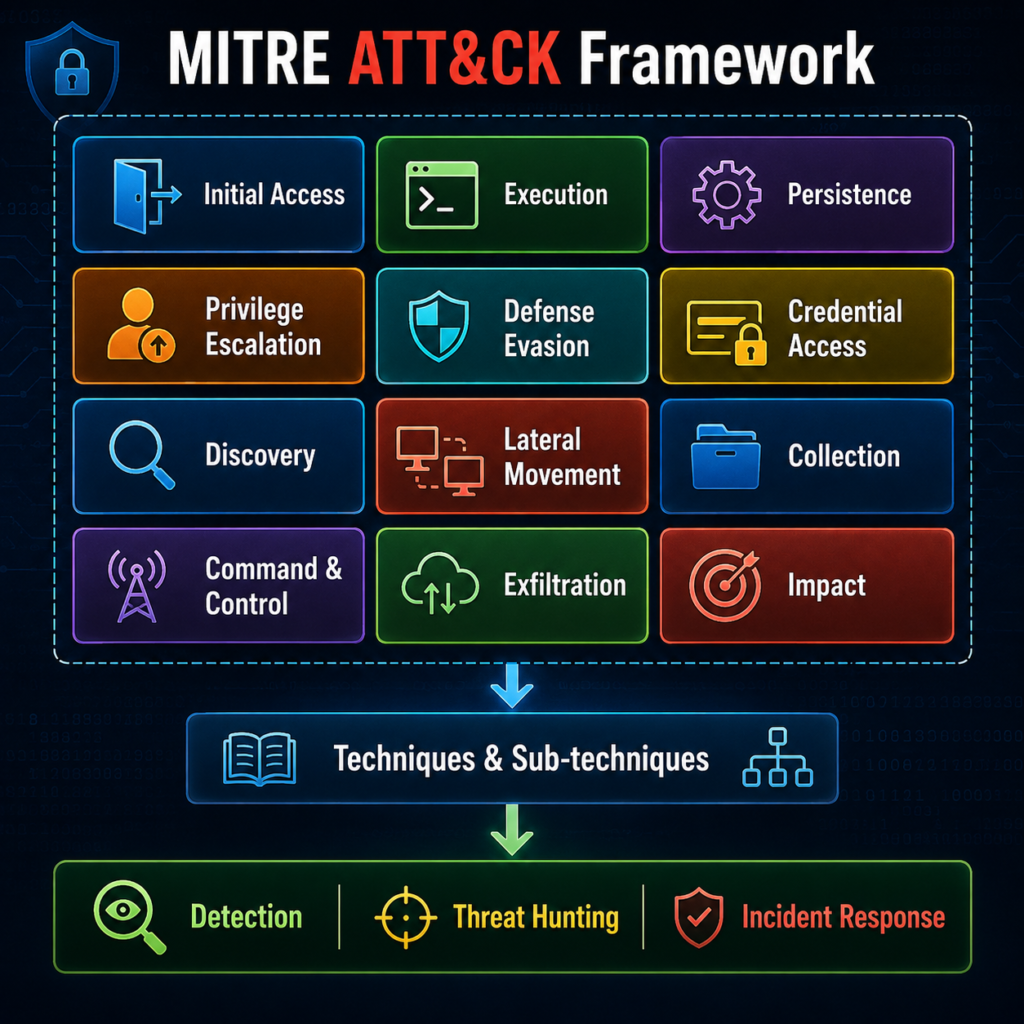
The framework categorizes cyberattacks into Tactics, Techniques, and Sub-techniques, enabling organizations to understand how attackers achieve their objectives and how to detect and mitigate these activities.
Architecture
Working
Step 1: Identify the Attacker’s Objective
Step 2: Map Techniques
Step 3: Collect Security Data
Step 4: Detect Suspicious Activity
Step 5: Investigate Incidents
Step 6: Respond to Threats
Step 7: Improve Security Controls
Advantages
MITRE ATT&CK offers numerous benefits to cybersecurity teams.
- Provides a standardized framework for understanding cyberattacks.
- Improves threat detection and monitoring.
- Enhances threat hunting capabilities.
- Strengthens incident response.
- Helps identify security gaps.
- Supports red team and blue team exercises.
- Improves SOC operations.
- Maps real-world attacker behaviors.
- Integrates with SIEM, EDR, and SOAR platforms.
- Widely accepted across the cybersecurity industry.
Disadvantages
Although highly valuable, the framework has some limitations.
- Requires experienced security professionals for effective implementation.
- Can be overwhelming for beginners due to its extensive knowledge base.
- Does not replace penetration testing or vulnerability assessments.
- Requires continuous updates to stay aligned with evolving threats.
- Mapping alerts to ATT&CK techniques may require significant effort.
- Organizations need mature logging and monitoring capabilities to maximize its value.
Tools:
| Tool | Purpose |
| MITRE ATT&CK Navigator | Visualize and map ATT&CK techniques |
| ATT&CK Workbench | Customize and manage ATT&CK knowledge |
| Microsoft Sentinel | SIEM with ATT&CK mapping |
| Splunk Enterprise Security | Threat detection and ATT&CK dashboards |
| IBM QRadar | Security analytics and event correlation |
| Elastic Security | ATT&CK-based detections |
| Wazuh | Open-source SIEM with ATT&CK integration |
| CrowdStrike Falcon | Endpoint Detection & Response (EDR) |
| Microsoft Defender for Endpoint | Endpoint protection with ATT&CK visibility |
| Cortex XSOAR | Security orchestration and response |
| TheHive | Incident response and case management |
| Caldera | MITRE’s adversary emulation platform |
Interview Questions
1. What is MITRE ATT&CK?
Answer:
MITRE ATT&CK is a knowledge base of real-world attacker tactics, techniques, and procedures (TTPs) used to improve threat detection, threat hunting, and incident response.
2. What does ATT&CK stand for?
Answer:
Adversarial Tactics, Techniques, and Common Knowledge.
3. What is the difference between a Tactic and a Technique?
Answer:
- Tactic: The attacker’s objective (e.g., Credential Access).
- Technique: The method used to achieve that objective (e.g., Credential Dumping).
4. Why is MITRE ATT&CK important?
Answer:
It provides a standardized framework for understanding attacker behavior, improving threat detection, enhancing incident response, and supporting threat hunting activities.
5. What is ATT&CK Navigator?
Answer:
ATT&CK Navigator is a visualization tool that helps organizations map ATT&CK techniques, assess detection coverage, and identify security gaps.
6. How is MITRE ATT&CK used in a SOC?
Answer:
SOC analysts use ATT&CK to map alerts to attacker techniques, investigate incidents, prioritize threats, improve detections, and develop response playbooks.
Conclusion
The MITRE ATT&CK Framework has become an industry standard for understanding and defending against modern cyber threats. By documenting real-world attacker tactics, techniques, and procedures, it enables organizations to improve threat detection, conduct effective threat hunting, strengthen incident response, and enhance overall security operations. Whether you’re a SOC Analyst, Threat Hunter, Penetration Tester, or Security Engineer, mastering MITRE ATT&CK is a valuable skill that can significantly improve your ability to detect and defend against sophisticated cyberattacks.
🚀 Master MITRE ATT&CK with SecureFlow Infotech
Take your cybersecurity skills to the next level with SecureFlow Infotech’s SOC, SIEM & Threat Hunting Training Program.
What You’ll Learn
- MITRE ATT&CK Fundamentals
- Tactics, Techniques & Procedures (TTPs)
- Threat Hunting Methodologies
- SIEM (Microsoft Sentinel & Splunk)
- Log Analysis & Event Correlation
- Endpoint Detection & Response (EDR)
- Incident Response
- Threat Intelligence
- Purple Teaming Concepts
- Real-Time SOC Labs & Hands-on Projects
Why Choose SecureFlow Infotech?
- ✅ Certified & Experienced Trainers
- ✅ Practical Hands-on Training
- ✅ Industry-Oriented Curriculum
- ✅ Real-Time Attack Simulations
- ✅ Placement Assistance
- ✅ Interview Preparation
- ✅ Online & Offline Training
- ✅ Flexible Batch Timings
📞 Contact Us:
+91 91339 19666
+91 91884 94949
Join SecureFlow Infotech today and gain the practical expertise needed to use the MITRE ATT&CK Framework for threat detection, threat hunting, and incident response, preparing you for a successful career in modern cybersecurity.